- Many organizations use Cybersecurity Awareness Month to launch internal education campaigns, but awareness is no longer their primary challenge.
- Organizations need ways to shift employee behavior so employees take greater individual responsibility for safeguarding the business.
- To change behavior, organizations should understand why employees avoid security controls and then find ways to reduce friction.
October is Cybersecurity Awareness Month—and chances are, you’ve been reminded of that fact a few times already. Because every year at this time, many cybersecurity companies publish familiar blog posts. They present best practices that should be deeply ingrained in everyone’s mind by now, such as using a password manager, enabling multi-factor authentication (MFA), and avoiding clicking on suspicious links.
These are important practices, but the yearly reminders are no longer as useful as they once were. Most organizations have heard the same messages for several years. They’ve also run internal awareness campaigns and implemented policies and tools that, in theory, should help reduce security incidents.
Still, there’s more work to be done. For example, organizations need to figure out why employees who are well aware of phishing continue to click on malicious links. And why some go out of their way to avoid adopting new security tools. This month is a perfect time to examine why awareness alone is not enough.
Moving Beyond Awareness to Responsibility
According to the U.S. Cybersecurity & Infrastructure Security Agency (CISA), Cybersecurity Awareness Month is a time when public and private sector organizations should come together to raise awareness about the importance of cybersecurity.1 For many organizations today, however, awareness is no longer the primary problem. Employees generally understand essential threats and recognize the importance of cybersecurity.
The problem is that these individuals believe cybersecurity is the responsibility of their employers. Employees rely on their security team and a variety of cybersecurity solutions to address threats. They don’t believe that they play an important role in turning the tide against attacks.
Another educational campaign is unlikely to change much. In fact, when organizations launch campaigns about identifying suspicious emails, they might inadvertently reinforce the belief that the organization “owns” cybersecurity. They define the problem and present the solution, usually in the form of new policies or tools. Employees just have to take some quizzes.
The challenge for organizations is to move beyond awareness, which is what those quizzes measure. Organizations need to get individuals to accept some responsibility for combating malicious activity. Part of that effort must include strategies for changing individual behavior.
Understanding Why Employees Don’t Adopt Controls
A low adoption rate for a cybersecurity tool or policy is a sign that employees are not taking individual responsibility for protecting their company. But that low adoption rate might have a somewhat understandable cause.
Employees often see security controls—such as new tools or policies—as impediments to their productivity. Let’s say an organization establishes a new policy that employees must use distinct passwords for each application or service. The employees might see that requirement as overly cumbersome and ignore it for as long as possible.
In some cases, employees invent workarounds rather than adopting new tools or policies. For example, a team might create a shared account for a SaaS app and then route MFA prompts to a shared password vault that auto-fills codes for everyone. The workaround avoids workflow disruptions, but of course, it reduces the effectiveness of MFA.
The first step for organizations is to determine where exactly the problem lies. Which policies are readily accepted? Which tools are underutilized?
Augmenting Awareness Metrics with Behavioral Ones
To pinpoint issues with cybersecurity controls, organizations should measure behavior. In addition to assessing the percentage of employees who passed a quiz on phishing awareness, they should collect metrics on actions. What percentage of employees have spotted and reported phishing incidents? What percentage are using a new tool meant to prevent account takeovers?
If only 20% of employees are using a new password management tool, for example, the organization’s leadership will know they have a challenge they need to address. Their priority should be finding the friction that is preventing employee adoption and then figuring out the best way to remove it.
On the other hand, if 95% of employees are using a one-click button integrated into their email application to identify phishing attempts, leaders might have a model they can draw from. What is it about that tool or its implementation that caused it to be more successful than others?
Running a 30-Day Friction Audit
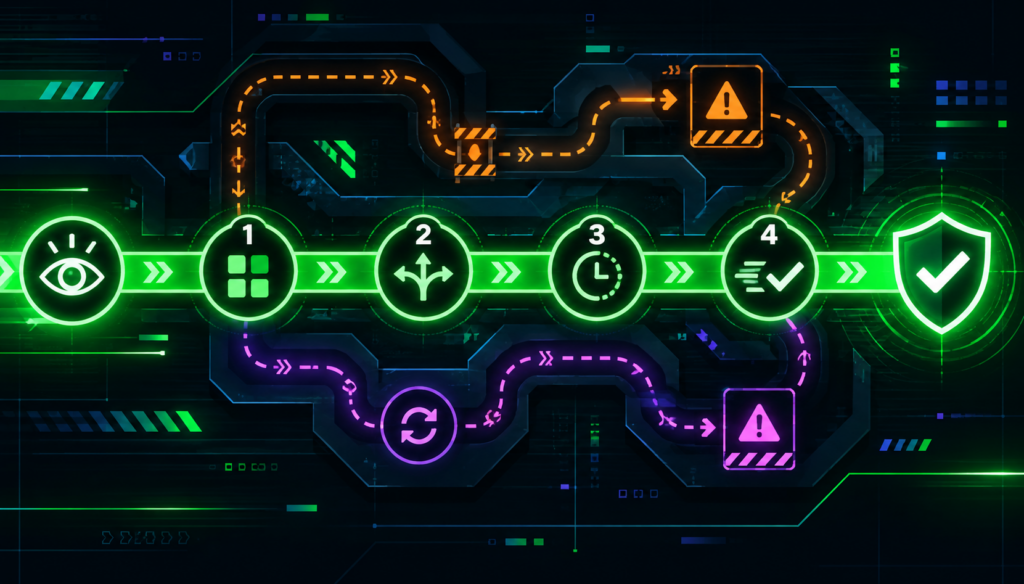
Once an organization has spotted some behavioral issues—namely, poor adoption of tools or policies—they need to find the best path for changing behaviors. Running a 30-day friction audit can help. The security team can determine which tools or policies are problematic, how processes have broken, and how to fix them.
In the first week, the security team should inventory the controls that users typically touch on a daily basis. For example, they might use MFA, password management, encrypted file transfers, or VPNs.
In week two, the team can find the workarounds that users have implemented to avoid those controls. The team could start by comparing license counts to active usage. Then, looking for shared accounts, examining usage of personal cloud storage, or finding forwarded emails could help determine whether and how employees are modifying workflows. Managers can help highlight ways that key processes break.
In the third week, security teams should time the friction. For example, they could measure how many seconds each control—when used correctly—adds to a workflow. They could then calculate how many times a day those moments occur. A new tool might add only a three-second prompt, but if that prompt appears 40 times per day, it can have a real impact on productivity. This is the types of delay that drives employees to develop a workaround.
In week four, it’s time to address the workaround. The best approach is to redesign the control so the secure path is the fast path. In other words, remove the need for a workaround. Alternatively, teams should document the workaround and at least ensure it doesn’t defeat the control.
Changing Behavior by Redesigning Workflows
Cybersecurity awareness is not sufficient for protecting organizations. Even employees who clearly understand the importance of safeguarding data and avoiding operational disruptions might neglect using security tools or fail to follow policies. Instead of focusing primarily on awareness, many organizations would benefit from facilitating shifts in behavior.
Security teams could redesign workflows to better incorporate new controls. Rather than mandating that employees force-fit new tools into their current processes, security teams can identify potential problems and then provide solutions that employees actually want to adopt. In the end, this approach will achieve greater behavioral change among employees—and deliver more lasting results for the company—than running another awareness campaign.
A: Cybersecurity Awareness Month, observed every October, is meant to bring public and private sector organizations together to raise awareness about the importance of cybersecurity. Many organizations review key best practices for their employees, but they might also use the opportunity to better understand why not all policies and tools are adopted.
A: In many cases, employees understand the importance of cybersecurity but do not take personal responsibility for protecting their organization. They fail to follow policies and avoid using tools that disrupt their established workflows.
A: Security teams should identify which policies or tools are suffering from poor adoption. They can then examine how those controls might disrupt workflows and determine how employees have been working around the controls. Instead of forcing a shift in employee behavior, teams can redesign workflows to reduce friction and encourage adoption.
- U.S. Cybersecurity & Infrastructure Security Agency (CISA), Cybersecurity Awareness Month Toolkit, August 2026
